DDoS-Protected VPS Hosting in 2026: Security, Mitigation and Buying Guide
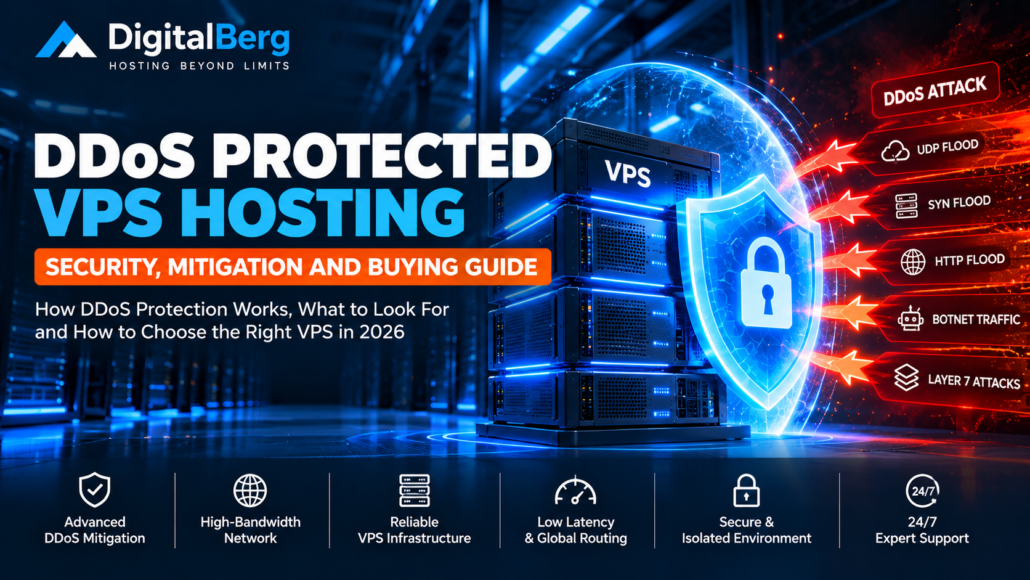
DDoS-protected VPS hosting combines the flexibility of a virtual private server with network and application defences designed to keep legitimate users connected during distributed denial-of-service attacks. In 2026, a secure VPS needs more than a firewall or a high-bandwidth port. Buyers should understand the attack types a provider mitigates, where filtering occurs, how applications are protected and what happens when an attack exceeds the contracted service limits.
This guide explains DDoS protection for VPS servers, compares network-layer and application-layer mitigation, shows practical Linux hardening steps and provides a checklist for evaluating hosting providers. It is intended for websites, APIs, SaaS platforms, ecommerce applications and game servers.
What Is DDoS-Protected VPS Hosting?
A DDoS-protected VPS is a virtual server supported by systems that detect and mitigate malicious traffic intended to overwhelm a service. The VPS still runs its own operating system and applications, but upstream infrastructure may inspect, filter, rate-limit or redirect traffic before it reaches the virtual machine. Protection capabilities vary significantly between providers and plans. A service advertised as DDoS protected is not necessarily immune to every attack.
Explore DigitalBerg VPS hosting for available virtual server configurations. Confirm the exact DDoS mitigation features and service limits for any plan before purchase.
How DDoS Attacks Affect a VPS
A distributed denial-of-service attack uses multiple sources to generate traffic or requests that exhaust a network, protocol stack or application. Even a VPS with sufficient CPU and RAM can become unreachable when upstream links saturate. Conversely, relatively modest traffic may disrupt a poorly optimised application if it forces expensive database queries or authentication operations.
Volumetric attacks: UDP floods and amplification
Volumetric attacks attempt to overwhelm available bandwidth. Reflection and amplification techniques can produce substantial traffic toward a target. Effective mitigation generally requires upstream network capacity and filtering; a firewall running only inside the VPS cannot restore connectivity after the provider’s upstream link is saturated.
Protocol attacks: SYN floods and connection exhaustion
Protocol attacks target network or transport-layer behaviour. SYN floods, for example, can exhaust connection-handling resources. Defences may include SYN cookies, connection tracking controls and upstream filtering, depending on the architecture.
Application-layer attacks: HTTP floods
Layer 7 attacks imitate application requests. They may target expensive URLs, login forms, search endpoints or APIs. A web application firewall, rate limiting, bot detection and application-specific controls are often more useful here than raw bandwidth capacity.
DDoS Protection Layers: What Actually Stops an Attack?
| Protection layer | Typical controls | Best suited to |
|---|---|---|
| Upstream network | Traffic scrubbing, routing, filtering | Large volumetric attacks |
| Transport/network edge | SYN protection, ACLs, connection limits | Protocol and connection floods |
| Reverse proxy / CDN | Caching, WAF, bot controls, rate limits | HTTP(S) services |
| VPS operating system | Firewall, service hardening, resource limits | Reducing local exposure |
| Application | Authentication, quotas, request validation | Expensive endpoints and API abuse |
These layers are complementary. For example, a reverse proxy can shield an HTTP application, but it does not automatically protect a game server using a different protocol. Likewise, a Linux firewall cannot compensate for an upstream link that is already overwhelmed.
Always-On vs On-Demand DDoS Mitigation
Always-on mitigation continuously routes relevant traffic through filtering infrastructure. It can reduce detection and diversion delays, although its latency and false-positive characteristics depend on the service. On-demand mitigation activates after an attack is detected, potentially requiring a routing or traffic-diversion change. Ask providers about activation time, routing architecture, false positives, supported protocols and incident visibility.
How Much DDoS Protection Does a VPS Need?
There is no universal attack-size threshold that guarantees safety. A provider may advertise a mitigation capacity measured in Gbps or Tbps, but the relevant questions are whether that capacity is shared, where filtering takes place, which protocols are covered and what limits apply to your specific service. For packet-intensive attacks, packets per second can matter as much as bits per second. For HTTP floods, requests per second and application cost are often more useful measures.
Evaluate the workload first: public website, API, game server, database or remote desktop. Then ask whether mitigation is available for the ports and protocols you actually use. A provider’s total network capacity should not be confused with guaranteed protection allocated to one VPS.
DDoS-Protected VPS vs Standard VPS
| Feature | Standard VPS | DDoS-protected VPS |
|---|---|---|
| Virtual CPU, RAM and storage | Yes | Yes |
| Basic host firewall | May be available | May be available |
| Upstream attack filtering | Not necessarily | Included to a defined scope |
| Layer 7 application protection | Separate configuration may be needed | May still require a separate WAF |
| Guaranteed immunity | No | No |
| Incident support | Depends on plan | Depends on plan and SLA |
DDoS protection should be evaluated as a specific service capability, not simply a label attached to a VPS plan.
How to Secure an Ubuntu VPS Against Common Attacks
The following steps improve general VPS resilience but do not replace upstream DDoS mitigation. Before changing firewall rules, ensure you have console access and allow the management ports your environment requires.
1. Update installed packages
sudo apt update
sudo apt upgrade
2. Configure a host firewall
For an Ubuntu web server, first permit SSH access using the actual management port and source restrictions appropriate to your setup. The following is a basic example for SSH on port 22, HTTP and HTTPS:
sudo ufw allow 22/tcp
sudo ufw allow 80/tcp
sudo ufw allow 443/tcp
sudo ufw enable
sudo ufw status verbose
Restrict SSH to known administrator IP addresses where practical. Avoid enabling a firewall before verifying that remote administration will remain accessible. See the Ubuntu firewall documentation.
3. Enable sensible web request limits
For NGINX, a request-rate zone can reduce repeated requests to selected endpoints. This is an example, not a universal production configuration:
# In the http context:
limit_req_zone $binary_remote_addr zone=perip:10m rate=10r/s;

# Inside an appropriate server/location block:
location /login/ {
    limit_req zone=perip burst=20 nodelay;
    proxy_pass http://127.0.0.1:8000;
}
Test rate limits carefully: shared NAT addresses, legitimate bursts and reverse proxies can cause false positives. If NGINX sits behind a trusted proxy, configure the real client IP correctly before applying per-IP limits. Refer to the NGINX limit_req documentation.
4. Harden SSH and administrative access
Use SSH keys, disable password authentication only after confirming key-based access works, remove unused accounts and apply least-privilege permissions. Restrict control panels, databases and internal APIs to trusted networks. Consider MFA for management interfaces where supported.
5. Monitor traffic and application health
Track interface throughput, packets per second, HTTP status codes, connection counts, CPU load and memory pressure. Alerts should distinguish a legitimate traffic spike from unusual request patterns. Keep logs with suitable retention and avoid exposing sensitive information.
Should You Use Cloudflare or Another Reverse Proxy?
A reverse proxy or CDN can help protect websites by absorbing traffic at distributed edge locations and applying WAF, caching and rate-limit rules. This is especially relevant for HTTP and HTTPS applications. It is not a complete solution for every TCP or UDP protocol. If attackers can directly reach the VPS origin IP, some protections may be bypassed; use appropriate origin-access controls and avoid unnecessarily exposing the origin address.
For architecture and mitigation concepts, see Cloudflare DDoS protection documentation and OWASP’s denial-of-service guidance.
DDoS Protection for Game Servers vs Websites
Game servers often use UDP or other non-HTTP protocols, making a standard website WAF insufficient. Prioritise protocol-aware filtering, stable routing, packet-loss performance and latency. For websites and APIs, prioritise HTTP request analysis, bot controls, rate limiting and origin shielding. For database services, do not expose the database port publicly unless strictly required; prefer private networking or authenticated tunnels.
Businesses requiring exclusive physical resources can also evaluate DigitalBerg dedicated servers, while teams seeking virtual infrastructure can review VPS hosting options.
How to Choose a DDoS-Protected VPS Provider in 2026
Check mitigation scope, not just headline capacity
Ask which attacks are covered: UDP floods, SYN floods, amplification, HTTP floods and application abuse. Confirm supported ports, protocols, maximum sustained attack conditions and whether mitigation is automatic.
Verify network performance and data-centre location
Low latency and predictable routing can be important for interactive applications. Check regional connectivity and where the VPS is physically hosted. See DigitalBerg data-centre information for infrastructure context.
Understand support and incident procedures
Clarify what the provider monitors, what customers can see in an attack report, how false positives are resolved and whether emergency support is included. A published uptime percentage does not necessarily guarantee protection against every DDoS event.
Compare full monthly costs
Evaluate vCPU, RAM, storage, backup, bandwidth, protection features, managed services and any extra mitigation charges. Avoid comparing plans solely by advertised attack capacity.
DDoS-Protected VPS Buying Checklist
- Confirm the specific DDoS attack types covered.
- Check whether protection applies to HTTP, TCP and UDP services.
- Ask about mitigation location, detection and activation times.
- Verify any attack-size, bandwidth or fair-use limitations.
- Check whether origin IP protection is possible.
- Review SLA exclusions, support hours and escalation procedures.
- Confirm backups, snapshots and recovery options.
- Evaluate latency, routing and physical server location.
- Compare total costs and the scope of managed support.
Frequently Asked Questions
What is a DDoS-protected VPS?
It is a virtual private server supported by traffic filtering and mitigation designed to reduce disruption from distributed denial-of-service attacks.
Does every VPS include DDoS protection?
No. Features vary by provider and plan. Basic firewall access is not the same as upstream attack mitigation.
Can a firewall stop a large DDoS attack?
A host firewall can reduce some unwanted traffic, but it cannot restore connectivity if upstream links are saturated. Network-layer filtering must occur before that bottleneck.
Does DDoS protection stop all attacks?
No service guarantees immunity. Coverage depends on attack characteristics, mitigation architecture, capacity and service conditions.
Is a CDN enough to protect a VPS?
A CDN or reverse proxy can help protect supported web traffic. Other protocols and exposed origin IP addresses may require separate controls.
Is DDoS protection important for gaming VPS hosting?
Yes, especially when servers are publicly reachable. Protocol-aware UDP protection, latency and packet-loss performance are key considerations.
Does DDoS protection slow down a website?
It depends on routing and filtering architecture. Some protection layers add processing or routing overhead, while caching at an edge network can improve web performance.
What is the difference between Layer 3/4 and Layer 7 protection?
Layer 3/4 mitigation focuses on network and transport traffic. Layer 7 protection analyses application requests such as HTTP, often using WAF and rate-limit rules.
Final Thoughts
Choosing DDoS-protected VPS hosting in 2026 requires evaluating real mitigation capabilities, network quality, application controls and support. Effective resilience usually combines upstream filtering with careful VPS configuration and application-level safeguards. Review DigitalBerg VPS hosting and confirm the protection scope of the specific plan before ordering.


Leave a Reply
Want to join the discussion?Feel free to contribute!